
Resources
Resources
Stay up to date with the latest news, opinions and free resources from Device Authority.
From company announcements, expert opinion on the latest IoT security issues or helpful guides to support your own organization, use our filters below to find the resources most useful for you.
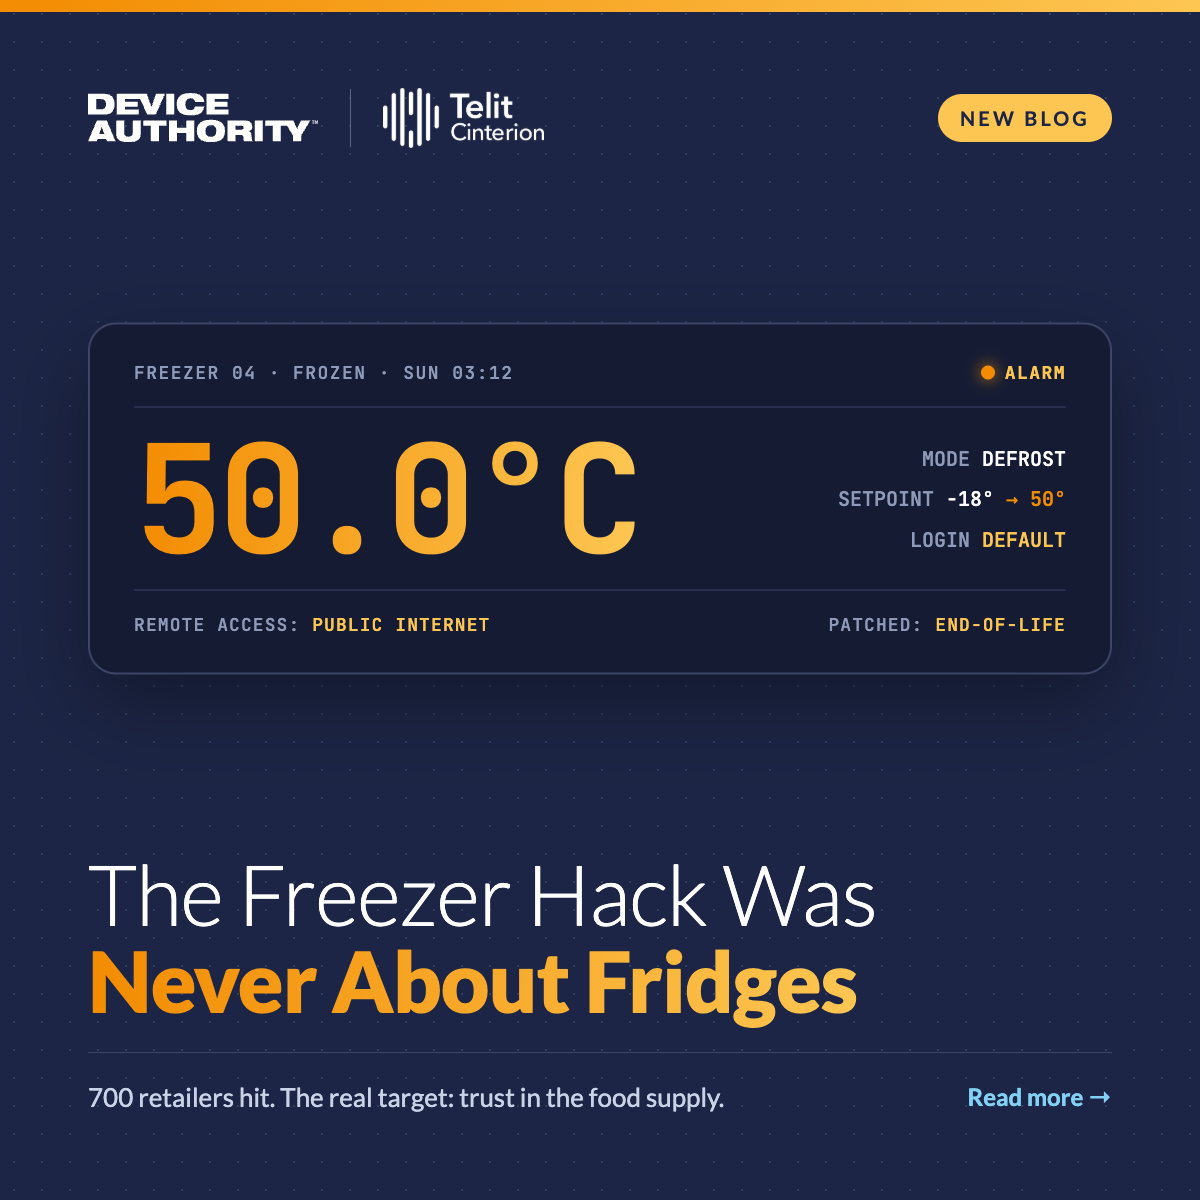
The Freezer Hack Was Never About Fridges
On the night of 11 October, someone switched hundreds of French supermarkets’ freezers into defrost mode and pushed the temperature to 50°C. By Monday morning, staff were opening freezer doors to blasts of hot air, pools of water and spoiled stock. Some stores caught fire. Around 700 food retailers were affected and single stores reported losses of several hundred thousand euros.
The timing was no accident either. A Sunday night meant closed stores, skeleton staff and maintenance contractors off shift. By the time anyone could respond, the damage was done, and the attack had played out in exactly the hours when nobody was watching.
It is tempting to file this under “strange cyber stories”. That would be a mistake. Nobody breaks into refrigeration controllers across a country to ruin some yoghurt. The freezers were the means. The target was something much bigger.
Blog
Read More
>
AI is learning to control machines…but can it trust them?
Anthropic’s new Model Hardware Standard (MHS) could mark an important step in the evolution of agentic AI.
Currently in research preview, MHS provides a standardized way for AI agents to discover, understand and operate physical equipment. Anthropic is already demonstrating the concept with laboratory and manufacturing equipment including robotic arms, microscopes, liquid handlers and laser systems.
The objective is compelling. Instead of spending weeks integrating different pieces of hardware, organizations could give AI agents a common interface through which they can orchestrate multiple machines.
But giving AI access to the physical world introduces a new security question….
Blog
Read More
>
Building the foundation for the Smart, Green Port
Many ports already operate hundreds or thousands of connected assets across multiple systems, suppliers and stakeholders. When these initiatives evolve independently, the result can be fragmented technology, siloed data, unclear ownership and growing complexity around security and compliance. As the whitepaper highlights, the challenge is increasingly not connectivity, but how that connectivity is governed and managed.
Download the whitepaper
Blog
Read More
>
You Shouldn’t Have to Predict the Future to Secure Your Devices
KeyScaler is moving to a usage-based model. Instead of licensing a fixed device count, you draw from a pool of credits that are consumed by the operations you actually perform — provisioning an identity, rotating a credential, enrolling a certificate, enriching a device record with vulnerability and SBOM intelligence.
Find out why we’re making the move and the benefits it brings
News
Read More
>

TechWorks Summit 2026
For the first time, NMI, DESN, AESIN and IoTSF unite to connect the full semiconductor-to-systems ecosystem. 600+ leaders in chip design, semiconductor manufacturing, electronic systems, cybersecurity, AI and compute will join together for TechWorks’ flagship 30th anniversary summit, delivered in partnership with the UK Semiconductor Centre.
Events
Read More
>
Device Authority Included as a Representative Vendor in Two Gartner® Hype Cycle™ Reports for 2026
Device Authority has been recognised as a Sample Vendor for IoT Authentication in both the Gartner® Hype Cycle™ for Digital Identity, 2026 and the Gartner® Hype Cycle™ for Zero-Trust Technology, 2026.
News
Read More
>
Legacy Medical Devices Aren’t Going Away: Why Healthcare Needs an Identity-First Security Strategy
Phil Englert recently highlighted an uncomfortable reality facing healthcare organizations: legacy medical devices remain one of the most significant cybersecurity risks in modern healthcare environments. Unsupported operating systems, limited security capabilities, patching challenges, and increasing cyber threats create a perfect storm for hospitals attempting to balance patient care, operational continuity, and cybersecurity.
The challenge is not new, but it is becoming more urgent.
Blog
Read More
>
Device Authority and Xalient Partner to Strengthen IoT Security for Enterprise Customers
Device Authority, a global leader in identity and access management (IAM) for IoT and OT devices, today announced a new strategic partnership with Xalient, a leading provider of identity‑led cybersecurity services and managed solutions.
The collaboration will strengthen Xalient’s IoT security offering through the integration of Device Authority’s KeyScaler platform, enabling scalable, automated protection for connected devices across complex enterprise environments.
News
Read More
>
Mandatory Cyber Incident Reporting Arrives in 2026: What It Means for Businesses and How to Prepare
This year marks a pivotal shift in global cybersecurity regulation. Mandatory cyber incident reporting is no longer a recommendation—it is a legal obligation.
Across major jurisdictions, regulations such as the EU’s Cyber Resilience Act (CRA), the NIS2 Directive, and the U.S. Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA) are introducing strict reporting timelines, expanded scope, and significant penalties for non-compliance. For many organizations, particularly those operating connected devices at scale, this represents a fundamental change in how cyber risk must be managed.
Blog
Read More
>